
A ransom note on a desktop, unfamiliar file extensions across a shared drive, or a NAS folder that suddenly will not open requires a calm response. To recover files after ransomware, the first priority is not finding a decryptor or restarting affected devices. It is stopping further encryption, preserving recovery options, and understanding exactly what has been affected.
Ransomware incidents can involve far more than visible documents. Attackers may encrypt local drives, mapped network shares, connected backup storage and cloud-synchronised folders. In business environments, they may also copy data before encrypting it. The right response depends on the device, the ransomware strain, the age and isolation of backups, and whether data has been removed from the environment.
Act first: contain the ransomware
If encryption is still occurring, immediately disconnect the affected computer or storage device from networks. Unplug the Ethernet cable, turn off Wi-Fi where possible, and disconnect external drives. For a NAS or RAID system, disconnect it from the network rather than repeatedly powering it on and off. Shutting a device down may be appropriate if files are actively being encrypted, but it can also remove useful evidence held in memory. If you are unsure, isolate it and seek specialist advice promptly.
Avoid these common reactions:
- Do not delete the ransom note, encrypted files or suspicious programs.
- Do not run cleanup utilities, defragmentation tools or random online decryptors.
- Do not reconnect the device to test whether it is working again.
- Do not write new files to an affected hard drive, SSD, USB device or memory card.
- Do not assume a connected backup is clean simply because it still appears accessible.
Take photos or screenshots of the ransom note, changed file extensions, warning messages and the time you first noticed the issue. Keep copies of any note, attacker contact details and unusual filenames. This information can help identify the ransomware family and guide the recovery approach.
Identify what is affected before attempting recovery
The visible damage is not always the full scope. A home user may have an encrypted external drive and cloud sync folder. A business may have one compromised workstation, a file server, a NAS, virtual machines and backups connected under the same credentials.
Start by documenting affected systems and accounts. Check whether shared folders can be opened from unaffected devices, but do so cautiously and without mapping infected storage to clean machines. Determine the last known time files were normal. This helps establish which backup point may be safe and whether recent work needs separate recovery efforts.
For organisations, IT staff should review account activity, remote access tools, administrator logins and backup logs. Ransomware commonly follows credential theft or an exposed remote access service. Restoring files without closing the original entry point can lead to another compromise.
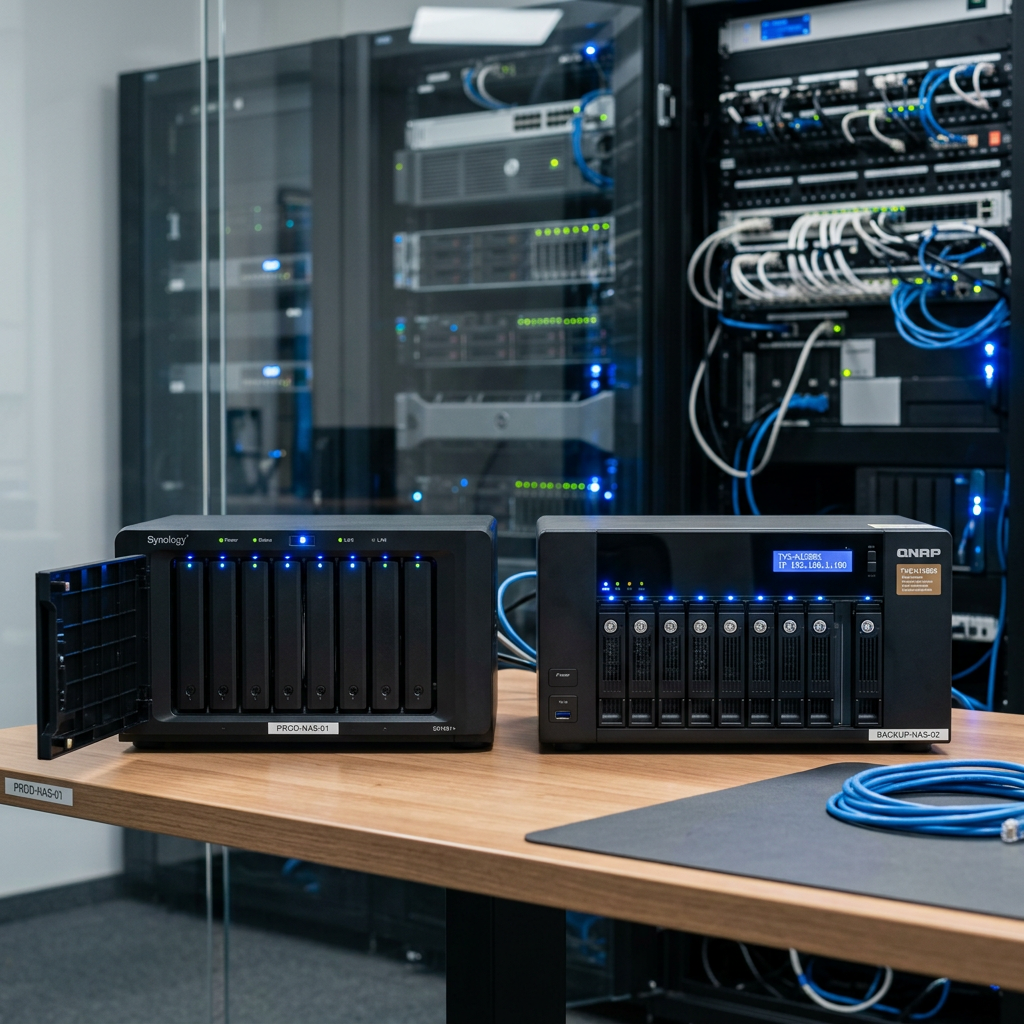
If a NAS, RAID array or server is involved, do not remove drives and attempt to rebuild the array yourself. RAID configuration information can be spread across member drives, and an incorrect rebuild can overwrite structures needed for recovery. Label each drive, keep its original order, and preserve the system in its current state until it can be assessed.
How to recover files after ransomware from backups
A clean, tested backup is usually the safest and most complete path to recovery. However, it must be checked before restoration. Ransomware can sit unnoticed for days or weeks before encryption begins, and attackers may attempt to delete, encrypt or tamper with backups first.
Look for backups that were offline, immutable, versioned or stored separately from the affected network. An offline backup is disconnected when not in use. Immutable storage prevents changes for a defined period. Versioned cloud backup services may retain earlier file versions, which can be valuable when the current version is encrypted.
Before restoring, scan the restored environment where practical and confirm that the infection route has been addressed. Recover files into a clean system or separate location first, rather than placing them straight back onto the original compromised device. Open a representative sample of documents, databases, photos and project files to confirm they are usable.
There is a trade-off between speed and certainty. Restoring everything from the newest backup may reduce downtime, but an older backup can be safer if there is evidence the attacker had access before the encryption event. For critical business systems, a staged restore is often sensible: restore essential services first, validate them, then recover less urgent data.
When there is no usable backup
No backup does not always mean no recovery option. The next step is to identify the ransomware strain and determine whether a legitimate decryption method exists. Some ransomware variants have known weaknesses, and security researchers occasionally release decryptors after obtaining keys or finding flaws in the encryption implementation. Many modern strains, however, use strong encryption and cannot be decrypted without the correct key.
Be wary of websites, tools or individuals that promise instant decryption for every attack. A poor-quality tool can damage encrypted files, overwrite recoverable data or introduce further malware. Never provide sensitive files, credentials or payment details to an unverified party.
File recovery may also be possible in limited circumstances where originals were deleted after encrypted copies were created. This depends heavily on the storage type and what happened after the attack. Traditional hard drives can sometimes retain deleted file data until it is overwritten. SSDs behave differently because TRIM and garbage collection may remove deleted data quickly. Continued use of either device reduces the chance of a successful recovery.
For photos, design files, office documents and other standalone files, specialist recovery work may locate remnants or earlier versions where the underlying data has not been fully overwritten. For databases, virtual machines and complex business systems, recovery can require careful analysis of file structures, snapshots, transaction logs and RAID configuration. Results vary, so a proper assessment should precede any promises about recoverability.
Should you pay the ransom?
Paying a ransom is a business, legal and risk decision, not a guaranteed recovery method. Payment does not ensure that a working key will be supplied, that every file will decrypt correctly, or that copied data will be deleted. It can also expose an organisation to further demands.
For businesses, involve executive decision-makers, cyber incident response advisers, legal counsel, insurers and relevant authorities early. Consider contractual notification duties and whether personal, customer or commercially sensitive information may have been accessed. The encryption of files is only one part of a potential data breach.
Home users should also avoid rushing into payment. Preserve the note and affected device, check for clean backups and obtain qualified advice about identification and recovery options. The apparent urgency in a ransom message is deliberate. Acting methodically gives you a better chance of protecting the data that remains.
Protect the device while recovery is assessed
Keep the affected storage media safe and unchanged. Do not reinstall the operating system, factory reset a NAS, initialise a RAID set, or format a drive in the hope that files will return. These actions can complicate recovery and remove forensic evidence of what occurred.
Where a device has mechanical symptoms as well as ransomware damage - clicking hard drives, drives dropping out, an SSD that is no longer detected, or a RAID reporting multiple failed disks - the situation needs extra care. Encryption may not be the only issue. A failing device can deteriorate with repeated power cycles, and logical recovery attempts should not take priority over preserving the physical media.
RecoveryGeeks can assess ransomware-affected hard drives, SSDs, NAS devices and RAID systems where deleted, damaged or inaccessible data may still have a recovery path. For Canberra customers and clients elsewhere in Australia, early assessment is particularly valuable when the affected device contains irreplaceable business records, creative work or personal files.
Rebuild with better recovery options
Once systems are clean and files are restored, improve the conditions for the next incident. Keep multiple backup copies, with at least one offline or otherwise protected from normal user access. Test restores regularly. A backup that has never been restored is an assumption, not a recovery plan.
Use multi-factor authentication for email, remote access and administrator accounts, keep operating systems and applications patched, and limit administrator permissions to the people who genuinely need them. Separate backup credentials from everyday user accounts. Small changes such as disabling unused remote access services and reviewing shared-folder permissions can materially reduce exposure.
The most useful action after discovering ransomware is often the least dramatic: isolate the affected system, stop making changes, and preserve every remaining recovery option. That discipline gives clean backups, specialist assessment and a safe rebuild the best possible chance to work.
