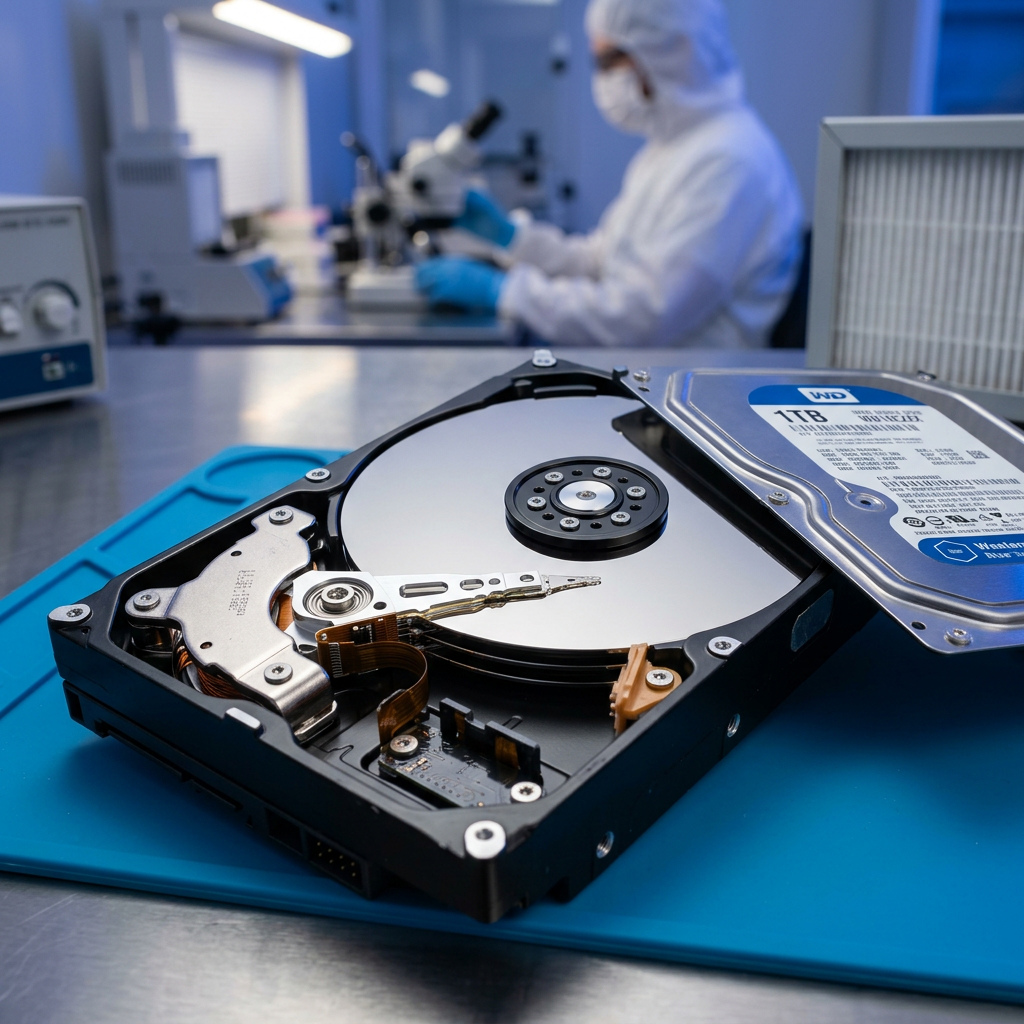

A failed drive can turn data privacy from a policy document into an immediate personal concern. The device handed over for recovery may contain family photos, tax records, client files, medical documents, passwords, business accounts or commercially sensitive work. Recovering those files matters, but so does knowing who can access them, why they need access and what happens to the data afterwards.
For Australian households and businesses, good data privacy is not just about stopping cybercriminals. It is also about making careful decisions when data is copied, stored, shared, repaired or recovered under pressure.
What data privacy means in a recovery situation
Data privacy is the right to control how personal or sensitive information is collected, used, stored and disclosed. In a data recovery job, that principle applies to the contents of the storage device as well as the device itself.
A hard drive, SSD, mobile, camera card or NAS unit is not simply a piece of hardware. It may contain information about people, finances, locations, communications and business operations. Even apparently ordinary files can reveal more than expected when viewed together. A folder of invoices may show customer details. A damaged laptop may retain browser data, saved passwords and correspondence. A photographer's memory card may hold images that have not yet been delivered to clients.
Recovery work often requires a technician to inspect file systems, identify recoverable data and verify that recovered files open correctly. That does not give a service provider free rein to browse through private material. The appropriate access should be limited to what is technically necessary to assess the device, perform the recovery and confirm the result.
The practical challenge is that a recovery cannot always be completed without some level of file visibility. A provider may need to check file names, types, folder structures or samples of recovered data to establish whether the outcome is useful. The key distinction is purpose: access should be controlled, documented and directed at the recovery task, rather than used for unrelated reasons.
Why privacy risks increase after data loss
Data loss creates urgency, and urgency can weaken good judgement. A business facing a failed RAID system may be unable to access accounting software or project records. A home user may be worried that years of photos have disappeared. In that moment, the first person offering a quick fix can seem like the obvious choice.
However, sending a device to an unknown party, installing unverified recovery software or sharing files through a personal cloud account can expose information further. The initial fault may be technical, but the consequences can become operational, financial or personal.
For businesses, the risk is broader than the lost files. Customer records, employee information, credentials, legal documents and intellectual property may all be present on the affected media. If the organisation is covered by the Privacy Act or has contractual confidentiality obligations, its responsibilities do not disappear because the data is inaccessible. Care is still required when engaging an external specialist.
There is also a technical trade-off. The quickest-looking option is not necessarily the safest. Repeatedly powering on a clicking hard drive, rebuilding a degraded RAID without a verified plan, or running software against a physically failing SSD can reduce the chance of a successful recovery. It can also lead to uncontrolled copies of sensitive data being created across multiple computers.
Questions to ask before handing over a device
A professional recovery provider should be able to explain its handling process in plain language. You do not need to be an IT specialist to ask sensible questions, particularly when the device contains confidential material.
Ask where the device will be assessed and recovered, whether work is performed locally or transferred elsewhere, and who may access it. Confirm how recovered data will be returned to you and whether an encrypted external drive is available or appropriate. It is also reasonable to ask how long working copies are retained after completion, how they are securely removed, and what happens if recovery is not possible.
For business devices, nominate one authorised contact. That person should be able to approve quotes, receive progress updates and collect recovered data. This avoids a stressful incident becoming a chain of informal requests from staff who may not have authority to make decisions.
Where a device contains especially sensitive information, provide only the background needed for diagnosis. Explaining that a NAS contains a virtual machine, database or critical design files is useful. There is rarely a need to send passwords, customer lists or detailed file contents by email unless the technician specifically requires them and provides a secure method for doing so.
Protect privacy before a device fails
The best recovery outcome is often a backup that makes recovery unnecessary. Backups are also a privacy control, provided they are managed properly. A copy stored on an unprotected portable drive or a shared account may solve one problem while creating another.
A practical approach is to keep more than one backup, with at least one copy separated from the main device. Encrypt portable backup drives, protect backup accounts with strong unique passwords and multi-factor authentication, and limit access to people who genuinely need it. For a small business, access to backup systems should not be shared casually across all staff.
It is worth checking whether backups can actually be restored. A backup that exists but cannot be opened, has not run for months or contains only partial folders can create a false sense of security. Periodic test restores are particularly valuable for business databases, accounting files, creative projects and NAS shares.
Device encryption is another worthwhile safeguard. If a laptop, mobile or external drive is lost or stolen, encryption can prevent someone from reading the contents without the correct credentials. But it comes with responsibility: if encryption keys or recovery passwords are lost, the data may be unrecoverable even when the hardware is physically intact. Store recovery keys securely and separately from the device.
What to do when privacy and recovery collide
If a device fails, stop using it where possible. Do not keep restarting a drive that is making unusual noises, and do not install recovery software onto the same drive that holds the missing data. For a mobile, camera card or external drive, avoid taking new photos, downloading files or saving new documents to it. Each new write can overwrite data that may otherwise be recoverable.
Then consider the sensitivity of the data alongside the recovery urgency. A home user might be primarily concerned with irreplaceable photos. A Canberra business may need to weigh downtime against the exposure of client data held on a failed server. In both cases, a clear chain of custody helps: record the device serial number, note who has possession of it, and keep it physically secure until it reaches the recovery provider.
If you suspect unauthorised access, ransomware or a lost device rather than simple hardware failure, treat the issue as a potential security incident. Change relevant passwords from a known-clean device, preserve evidence where possible, and seek IT or security advice before making broad changes to affected systems. Wiping, resetting or reformatting a device may remove evidence and can make recovery much harder.
For organisations, communicate carefully. Staff and clients need accurate information, but speculation can cause unnecessary alarm. Identify what data may be affected, who is responsible for the response and whether notification obligations apply. The right response depends on the facts, including whether the information was encrypted, whether it was accessed and the likely risk of serious harm.
Choosing specialist help without surrendering control
A specialist recovery service should reduce uncertainty, not add to it. Look for a provider that can discuss the type of media involved - from conventional hard drives and SSDs to Apple devices, camera cards, NAS units and RAID arrays - while being clear about process and limitations.
No reputable provider should guarantee recovery before assessing the device. Some failures are recoverable; others involve severe physical damage, overwritten data, encryption or controller faults that limit what can be retrieved. Straight answers about those limits are part of trustworthy service.
It also helps to separate the recovery decision from the wider clean-up work. Once files are returned, review what was exposed on the affected device, move the data to a secure destination, change credentials that may have been stored on it and retire unreliable media. RecoveryGeeks can assist with the recovery stage, but long-term privacy also depends on how recovered data is handled after it comes back to you.
Your files may be inaccessible, but they are still yours. Choose recovery support that treats that fact as seriously as the technical challenge of retrieving them.
