
A drive can be physically healthy, show every folder name, and still leave its owner unable to open a single document. This is the difficult reality behind the question, can professionals recover encrypted files? Sometimes, yes. But successful recovery depends less on the recovery software used and more on whether the encryption keys, passwords, recovery information or a valid copy of the data still exist.
Professional data recovery can solve many causes of inaccessible data, including failed hardware, corrupted file systems, damaged RAID arrays and accidental deletion. Encryption changes the equation. It is designed to ensure that data remains unreadable without the correct credentials. A legitimate recovery specialist can work around storage failure and corruption, but cannot simply bypass properly implemented modern encryption.
Can Professionals Recover Encrypted Files Successfully?
The honest answer is: it depends on what has failed.
If you know the password, have a recovery key, or can access a device that is still authenticated, a professional may be able to recover the encrypted files even when the drive itself is damaged. In this situation, encryption is not necessarily the problem. The problem may be a failing hard drive, an SSD controller fault, damaged partitions, file system corruption or a NAS with multiple failed disks.
For example, a BitLocker-encrypted Windows drive may stop booting after a hardware failure. If the BitLocker recovery key is available, a specialist can create a controlled clone of the failing drive, stabilise the physical media where possible, and work towards accessing the data without repeatedly stressing the original device. The same principle applies to FileVault-protected Apple devices, encrypted external drives and encrypted volumes used in business environments.
Where the only copy of the files is encrypted and no password, recovery key, authorised device session or backup exists, the prospect is very different. Strong encryption such as AES is specifically built to resist guessing and brute-force attacks. Attempting millions or billions of password combinations is not a practical recovery method for a well-chosen password.
A reputable provider should be clear about this limitation. Promising to “crack” any encrypted drive is not a sign of advanced capability. It is usually a warning sign.
The Difference Between Encryption and Data Corruption
People often describe any inaccessible file as “encrypted”, but several separate problems can produce a similar message on screen. Understanding the difference helps determine the next step.
A file system may be corrupted, making a folder appear empty or prompting Windows or macOS to format a drive. A hard drive may have bad sectors and be unable to read the portion of the disk containing the encryption metadata. A RAID or NAS may fail because its disk order, controller configuration or volume structure has been lost. In each case, the data may still be encrypted, but recovery can be possible if the correct credentials are retained.
Ransomware is different again. Ransomware encrypts files without the owner’s authority, often changes file names or extensions, and may leave a ransom note. The original password for the computer or cloud account will not decrypt ransomware-affected files. Recovery options may include clean backups, unaffected snapshots, previous file versions, recovered copies from other storage locations, or a verified decryptor where one exists for that ransomware strain.
Do not assume a ransomware payment guarantees recovery. Payment may not result in a working decryptor, may restore only some files, and can expose an organisation to further risk. Contain the incident first, preserve evidence, and obtain qualified cyber incident advice alongside any data recovery assessment.
When Recovery Has a Realistic Chance
Encrypted data recovery is most viable when a key component of access remains available. This might be the password itself, a BitLocker recovery key stored in a Microsoft account or workplace directory, a FileVault recovery key, a recovery key held by an IT administrator, or an accessible backup.
It can also be possible when the device remains unlocked. A laptop that is powered on and logged in may still have the decryption key available in memory or be able to read the encrypted volume normally. Turning it off, restarting it, or allowing its battery to go flat can remove that access. If the data is urgent and the device is open, avoid making changes and seek professional guidance before shutting it down.
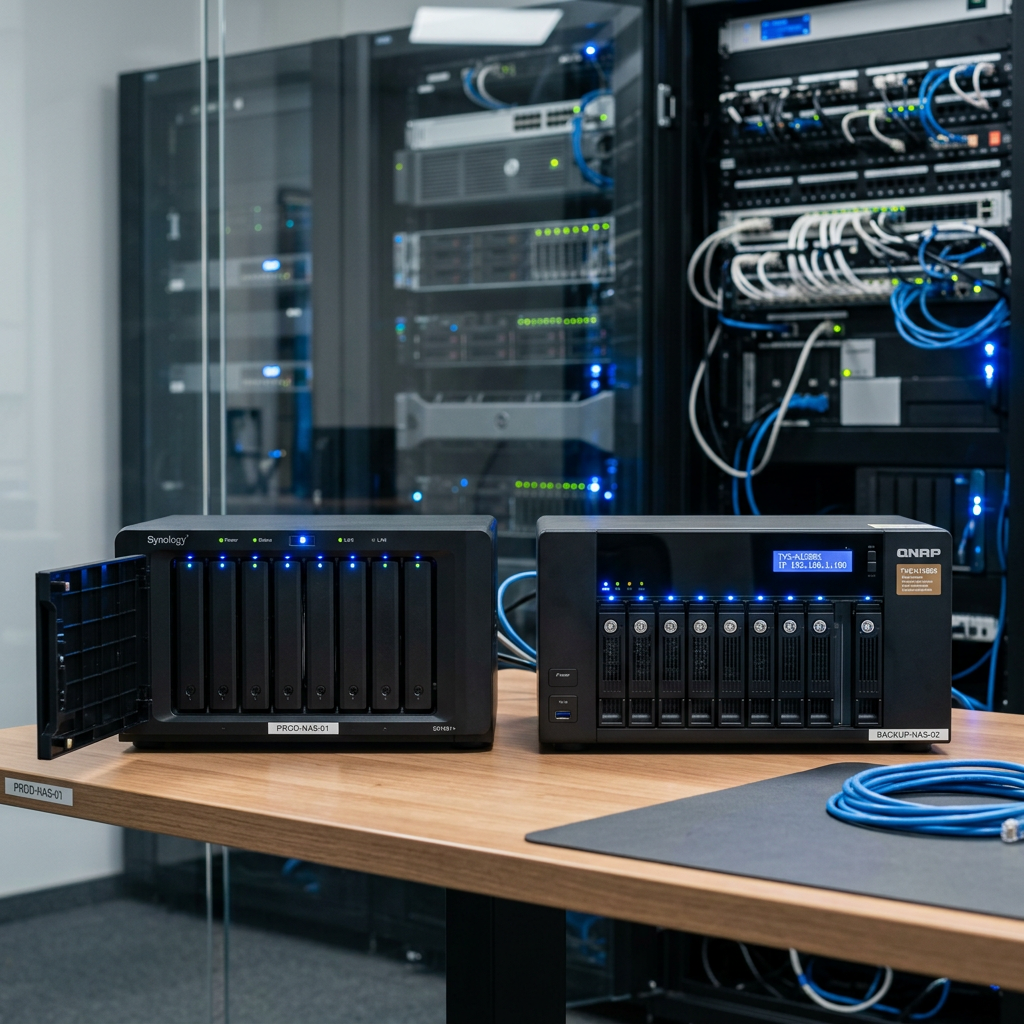
For business systems, access may depend on more than one item. An encrypted NAS or RAID can require the correct disk set, RAID configuration, encryption passphrase, key files and sometimes a functioning enclosure or management account. Rebuilding or initialising the array without confirming the configuration can overwrite critical metadata.
Deleted files are another case where the answer varies. If files were deleted from an encrypted drive but the volume can still be unlocked, recovery may be attempted from a forensic copy of the storage media. However, SSDs and many modern storage systems use TRIM and internal garbage collection, which can permanently remove deleted blocks quickly. Speed matters, but careless DIY recovery attempts can reduce the remaining options.
What a Professional Recovery Process Involves
A specialist does not start by guessing passwords or running repair tools directly against an original drive. The priority is to preserve the best available evidence and avoid further changes to the media.
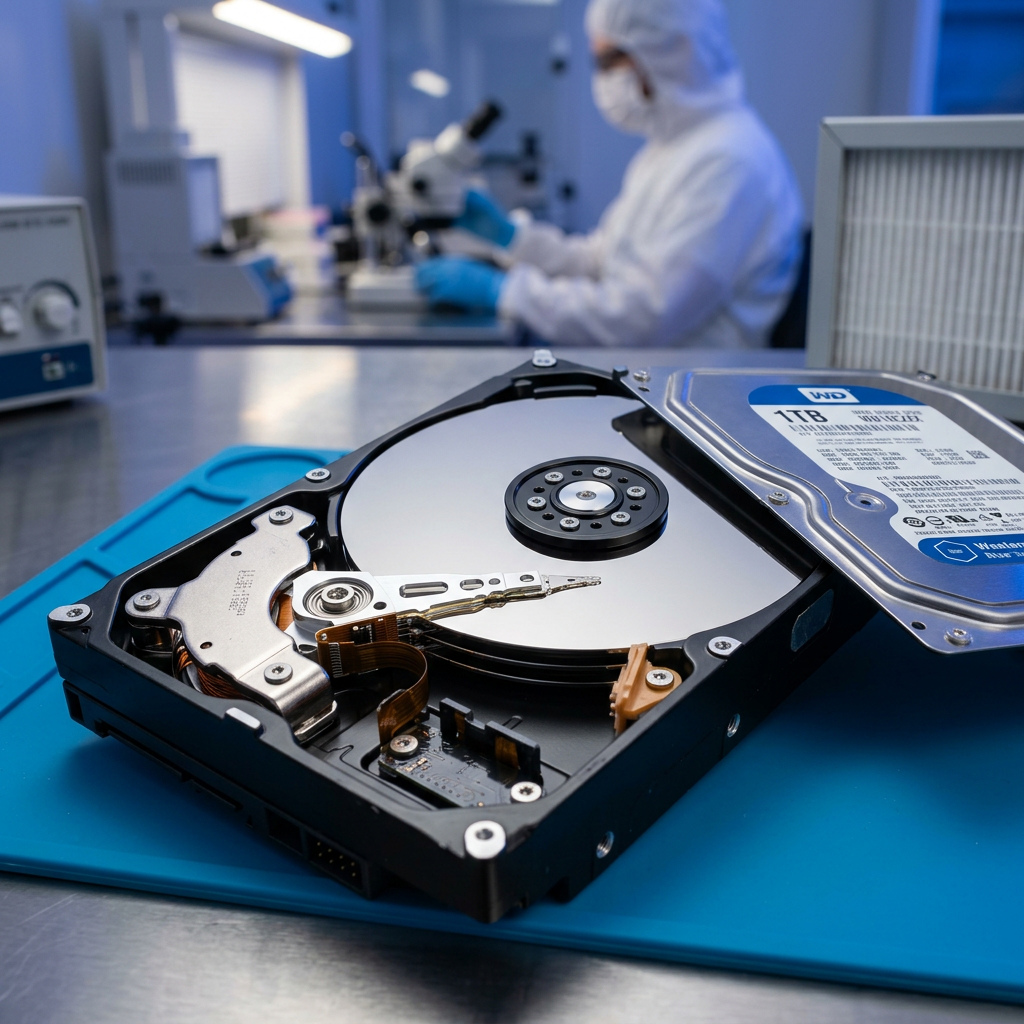
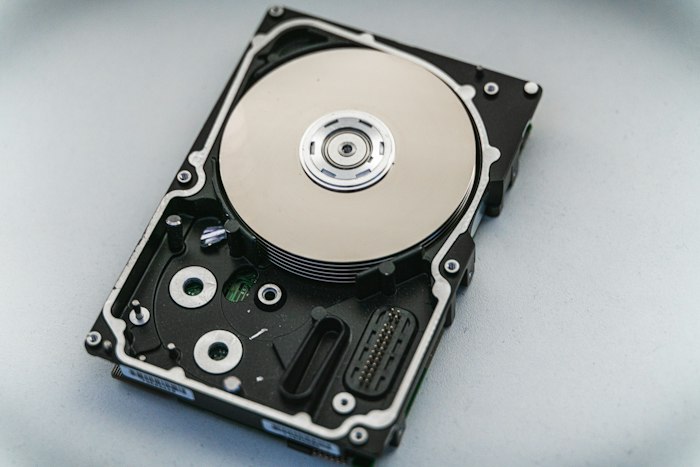
For a physically failing hard drive, this may involve controlled hardware work and imaging the disk sector by sector. With a damaged SSD, recovery can be more complex because wear levelling, encryption built into the controller and proprietary chip behaviour affect how data is stored. Apple devices also present specific challenges, as hardware-backed encryption can be closely tied to the original logic board and device passcode.
Once a stable copy is available, the recovery work focuses on the actual point of failure. That may mean reconstructing a corrupted partition, rebuilding a RAID virtually, locating missing encryption headers, extracting accessible files from an unlocked volume, or restoring data from an intact backup set.
Credentials should be handled carefully. A recovery provider may need a password or recovery key to validate access to the recovered data, but should explain why it is needed, how it will be used, and how it will be protected. For sensitive personal, legal, financial or business material, confidentiality and controlled handling are part of the service, not an afterthought.
What to Do Before You Try Anything Else
The first few decisions after encrypted data becomes inaccessible can make a significant difference. Avoid formatting the device, reinstalling an operating system, running “repair” utilities, or creating a new RAID volume over the old one. These actions may alter the metadata needed to reconstruct the storage or access the encrypted volume.
Write down any error messages and note what changed immediately before the issue occurred. Was the device dropped? Did the system ask for a BitLocker key after an update? Did a NAS lose power? Did the files gain unusual extensions and a ransom note appear? These details help distinguish a hardware issue from corruption, account access problems or ransomware.
Then gather the access information you have without repeatedly testing passwords. Check password managers, printed recovery records, Microsoft or Apple account recovery sections, IT documentation, old emails and business key-management records. If a staff member set up the encryption, establish whether they used a personal account, a workplace account or a shared administrative process.
Keep the affected device disconnected from the network if ransomware is suspected. For a failed external drive, NAS or RAID, power it down rather than repeatedly reconnecting it to see whether it appears. Repeated spin-up attempts can worsen a mechanical hard drive failure.
Password Recovery Is Not the Same as File Recovery
There are limited situations where password recovery work may be considered, such as when an owner remembers part of an old password pattern or has records that narrow the possibilities. Even then, success depends on the encryption type, password complexity and available information. It should never be presented as certain.
This distinction matters because passwords protect more than files. They may be tied to account access, business systems and personal identity. Any attempt to recover access must be lawful, authorised by the data owner and handled with appropriate privacy safeguards.
For most customers, the more productive question is not “Can someone break this encryption?” It is “Where might the legitimate key, unlocked session or unaffected copy still exist?” That shift often leads to the fastest, safest path to the data.
Encryption is doing its job when it prevents unauthorised access. When hardware fails or files disappear, the goal is to preserve that security while recovering what remains accessible. If you retain the correct credentials or recovery key, expert professional data recovery may still be a practical option. If you are unsure what has happened to an encrypted drive, mobile, NAS or RAID system, acting carefully now gives RecoveryGeeks the best chance to assess the situation without adding to the loss.
