
A ransomware incident becomes far more damaging when the first response overwrites evidence, spreads encryption to backups, or restores infected data straight back into production. The best practices for ransomware recovery start with containment and careful decision-making, not immediately trying every available fix.
For a Canberra business, a remote team, or a home user with irreplaceable files, the goal is the same: stop further damage, establish what has happened, and recover only from data and systems you can trust. The right approach will vary with the device, the type of ransomware, and the quality of available backups, but the principles below apply across most incidents.
Isolate affected systems immediately
If you suspect ransomware, disconnect the affected computer, server, NAS, or external drive from networks and shared storage as quickly as possible. Unplug the network cable, disable Wi-Fi, disconnect VPN access, and remove mapped network shares where practical. Do not reconnect the device simply to check whether it is working.
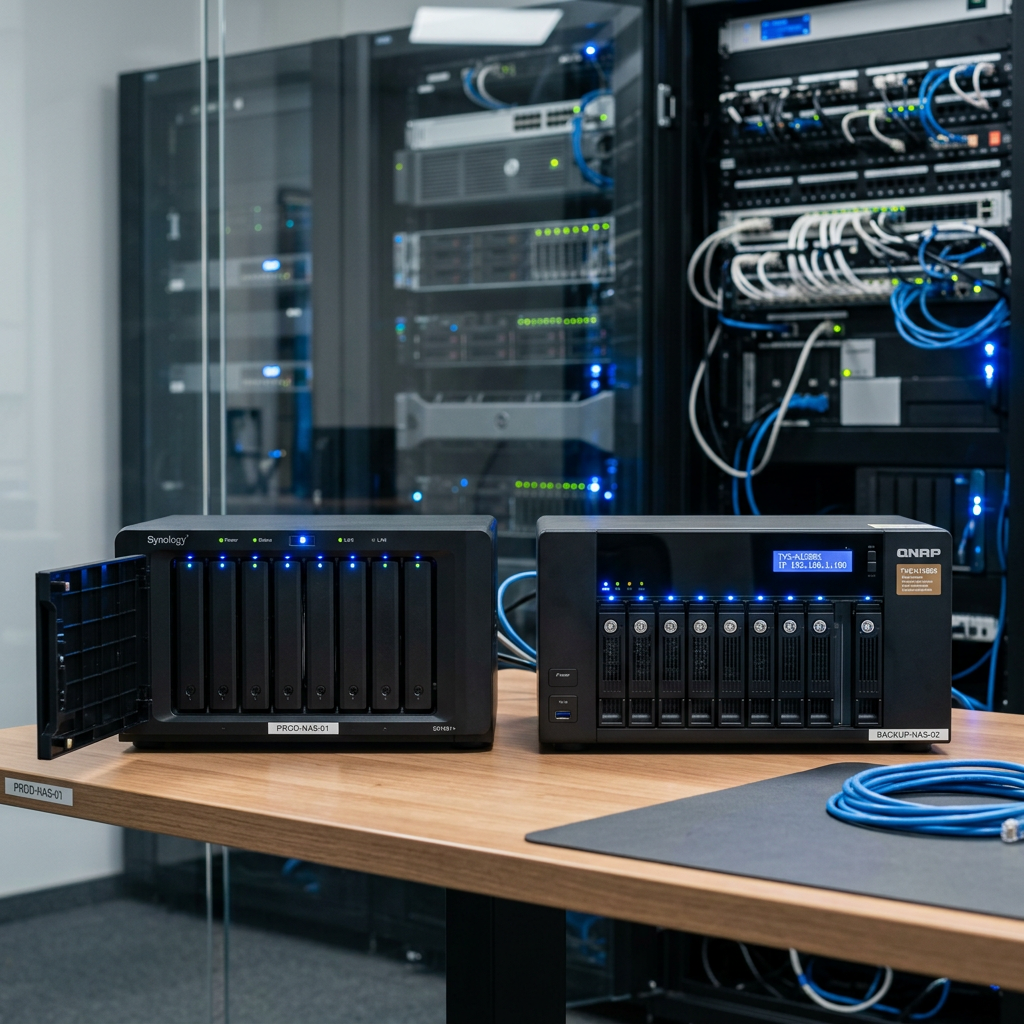
Isolation is particularly important for NAS and RAID environments. One compromised workstation with write access to shared folders can encrypt data across multiple volumes in a short period. Temporarily restrict access to file shares and cloud synchronisation services until the scope of the incident is known.
Do not rush to power off every device. A running system can contain valuable forensic information, including active processes, network connections, encryption notes, and memory-resident evidence. If encryption is actively progressing, isolation takes priority. If the device is already disconnected and stable, seek advice before rebooting, wiping, or running repair tools.
Preserve the evidence before changing anything
Ransom notes, file extensions, screenshots, email messages, suspicious attachments, timestamps, and security alerts can help identify the ransomware family and the likely entry point. Copy this information to a clean device or document it with photos if access is limited.
Keep a record of what you observe: which user accounts were affected, when files were last known to be accessible, which shared folders changed, and whether backup jobs ran successfully. This record helps IT staff, cyber security responders, insurers, and recovery specialists make informed decisions.
Avoid deleting the ransom note or encrypted files. Even where a decryptor may later become available, it will usually need samples of the encrypted data. Deleting material also makes it harder to determine whether the incident involved data theft as well as encryption.
Assess the scope, not just the visible damage
Ransomware rarely affects only the first device where it is discovered. Check endpoints, servers, virtual machines, cloud storage, email accounts, backup consoles, remote desktop services, and administrator accounts. Review logs where available to identify unusual sign-ins, privilege changes, failed login attempts, or large volumes of file activity.
A locked computer is obvious. Compromised credentials are not. If an attacker has obtained administrator access, they may have disabled backups, created new accounts, or accessed sensitive data before triggering encryption. That changes the recovery plan because restoring files alone does not remove the risk.
For businesses, involve your internal IT team or an experienced incident response provider early. If personal, financial, health, or customer information may have been accessed, obtain appropriate legal and privacy advice. Australian organisations may have notification obligations depending on the nature and scale of the breach.
Best practices for ransomware recovery from backups
Backups are only useful if they are separate from the compromised environment and can be restored safely. Before beginning a full restore, confirm when the backup was created, whether it is complete, and whether the ransomware may have been present when that backup was taken.
The most reliable backup strategy follows the 3-2-1-1 principle: keep at least three copies of important data, on two different types of storage, with one copy held off-site and one copy that is offline or immutable. Immutability means the backup cannot be altered or deleted for a defined retention period, even by a compromised administrator account.
Do not assume a cloud-synchronised folder is a backup. Synchronisation can replicate encrypted or deleted files quickly. Cloud services may offer version history and recovery options, but these need to be checked and configured before an incident occurs.
Restore into an isolated environment first wherever possible. Open a sample of restored documents, databases, images, and application data. Confirm that files are readable, current enough for operational needs, and free from suspicious changes. A staged recovery takes longer than copying everything back at once, but it reduces the chance of reintroducing malware or corrupt data.
Rebuild compromised systems from a known-clean state
Recovering files and recovering a trustworthy operating environment are different tasks. A system that has been compromised should not simply have its encrypted documents replaced and then be returned to normal use.
For business systems, rebuild affected machines from trusted installation media or a verified clean image. Apply operating system and application updates, reinstall essential software, and restore data only after the environment has been checked. For virtual infrastructure, verify the integrity of hypervisors, management consoles, and backup credentials before restoring workloads.
Reset passwords for affected accounts, beginning with administrator, backup, email, remote access, and service accounts. Use unique passphrases and multi-factor authentication. Review account permissions at the same time. Many ransomware incidents spread further than necessary because staff accounts have broad access to shares or systems they do not need for their role.
Treat NAS, RAID and external storage carefully
Do not initialise, format, rebuild, or replace drives in a NAS or RAID system simply because the data is inaccessible. Ransomware encryption is often a logical data problem, but hurried repair attempts can create a separate physical or structural recovery problem.
RAID arrays depend on the correct drive order, controller configuration, RAID level, stripe size, and file system structure. Rebuilding an array with the wrong assumptions can overwrite parity or metadata that may be required to recover data. Similarly, repeatedly powering up a failing hard drive or SSD can worsen physical faults.
If the incident involves a damaged drive, failed NAS, RAID degradation, or files that cannot be restored from backup, stop using the affected media. A specialist service such as RecoveryGeeks can assess storage devices and recovery options without unnecessary changes to the original data.
Decide carefully about ransom demands
Paying a ransom is not a recovery strategy. Payment does not guarantee a working decryption key, complete data restoration, or the deletion of stolen information. It can also expose an organisation to further demands or legal and financial complications.
That said, the decision is sometimes made under severe operational pressure. If a business is considering payment, it should obtain legal, cyber insurance, and specialist incident response advice first. Preserve evidence, verify the ransomware family, and investigate available backups and known decryptors before assuming payment is the only path.
Test your recovery plan before an incident
The most valuable ransomware recovery work happens before an attack. Test restoration of a representative set of files, a complete workstation, a server, and any critical business application. Measure how long each recovery takes. A backup that exists but needs three days to restore may not meet the needs of a business that depends on same-day access to customer records or project files.
Document who can isolate systems, who has access to backup credentials, where clean installation media is held, and how staff should report suspicious emails or device behaviour. Keep this plan accessible outside the main network, including offline contact details and recovery procedures.
Ransomware recovery is rarely just about getting files back. It is about returning to operations with confidence that the data is sound, the systems are clean, and the same weakness will not be used again. Calm containment, verified backups, and careful rebuilding give you the strongest path back from a disruptive incident.
