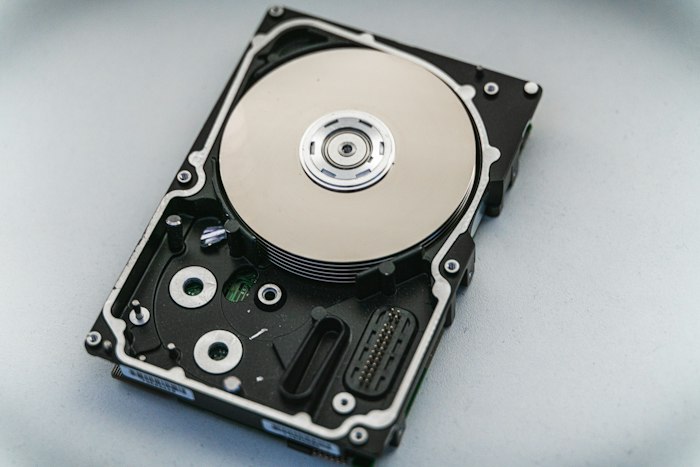

A failed drive can contain far more than documents. It may hold family photos, client records, financial information, legal files, medical correspondence or the only copy of a business database. When you hand that device to a recovery specialist, a reasonable question follows: are recovered files confidential?
They should be. A professional data recovery provider treats the information on a storage device as private customer data, not as material to browse, copy or retain. However, confidentiality is not something to assume without asking questions. It depends on the provider’s processes, the scope of the work, and the controls used from the time your device is received until your recovered data is returned.
Are recovered files confidential during data recovery?
In a professional recovery process, confidentiality applies to both the physical device and the recovered files. Technicians need limited access to data to confirm that recovery has succeeded and that the requested folders or files can be opened. That does not mean they need to review the contents of every document, image or database.
Most validation is technical. A specialist may check file structures, confirm that a drive image is complete, test whether a selection of recovered files opens correctly, or verify database integrity. The aim is to establish whether the data is usable, not to inspect its personal or commercial content.
The distinction matters. A provider recovering accounting records from a failed SSD may need to confirm that the accounting files are present and readable. They do not need to examine every transaction within them. Likewise, a camera card recovery can confirm that image files have been restored without treating the images as anything other than private customer property.
For sensitive matters, ask the provider how access is restricted and whether technicians are bound by confidentiality obligations. A clear answer is a good sign. Vague assurances are not enough when the device contains customer information, commercially sensitive work or irreplaceable personal files.
What a secure recovery process should look like
Confidentiality starts before any files are recovered. Devices should be logged when received, labelled with a job reference, and kept in a controlled workspace. This creates accountability and reduces the risk of a drive being misplaced or handled by people who are not involved in the job.
During recovery, the original media is normally treated carefully, particularly if it has physical damage. Technicians often work from a sector-by-sector clone or forensic-style image where possible, preserving the original device and limiting unnecessary handling. This is also good recovery practice: repeated attempts on a failing drive can make a recoverable problem worse.
Recovered data should be stored only for the time needed to complete the work and return it to the customer. It should be held on controlled systems rather than personal devices, removable media of uncertain origin, or open network locations. Access should be limited to authorised staff who need it to perform the recovery or quality checks.
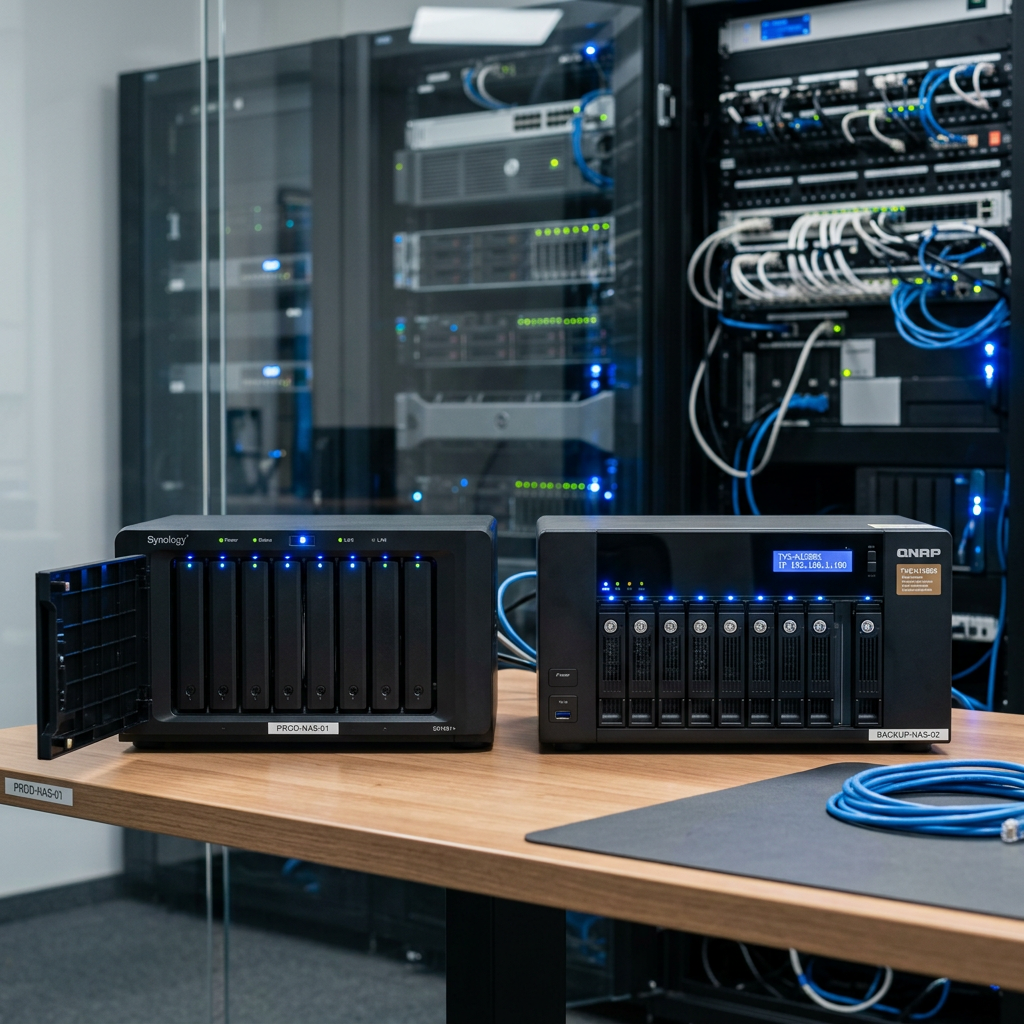
Secure return matters as well. If the data is supplied on a replacement drive, that drive should be prepared specifically for the job. If an electronic transfer is offered, ask how it is protected, how long the files will remain available, and whether you can set or receive a password separately. For large recovery jobs, such as NAS or RAID arrays, a physical encrypted drive may be more practical than transferring many terabytes online.
At RecoveryGeeks, the recovery objective is straightforward: retrieve your data with the care expected of a specialist service. For customers, that should include understanding how the device, working copies and final recovered data are handled at each stage.
When technicians may need to view file information
There are legitimate technical reasons a recovery technician may see limited file information. File names, folder structures, extensions, dates and sizes can help identify the correct volume, determine whether an attempted recovery has worked, and locate the material a customer has asked for.
A technician may also need to open a small sample of files to verify usability. A recovered Word document that will not open, or a video file that stops after a few seconds, is not a successful recovery simply because it has a familiar filename. Sample checks help identify corruption and guide further work.
This should be proportionate to the job. If you only need one project folder from a damaged external hard drive, tell the provider. If a business needs a specific virtual machine, accounting database or shared drive restored first, identify it at the outset. A defined recovery scope can reduce unnecessary processing and help prioritise the most valuable data.
Confidentiality risks to discuss before booking
No technical service can promise absolute risk-free handling, but a reputable provider should be able to explain its safeguards honestly. Before handing over a device, ask what happens to your data after recovery, who can access it, and how long copies are retained.
It is also worth asking whether the business uses confidentiality agreements for staff and whether it can sign a non-disclosure agreement for a particularly sensitive matter. Many organisations have their own privacy, procurement or legal requirements. Raising these before work begins avoids delays when the recovery is urgent.
For business customers, clarify the chain of custody. This is particularly relevant where the device contains employee records, client data, legal evidence, intellectual property or material subject to contractual obligations. Keep a record of the device serial number, what was supplied, the date it was transferred, and the person or courier responsible for it.
If you are sending media from outside Canberra or elsewhere in Australia, package it securely and use a tracked service. Do not write passwords on the device or place them in the same parcel. Provide credentials through a separate agreed channel only when they are needed. If the device is encrypted with BitLocker, FileVault, VeraCrypt or another system, recovery may not be possible without the correct recovery key or password.
Privacy, encryption and legal limits
Encryption is one of the strongest protections available because it can prevent anyone from reading the data without the necessary key. It can also complicate recovery. A specialist may be able to repair the storage device or retrieve an encrypted volume, but cannot reliably turn encrypted data into readable files without valid credentials.
Do not attempt to remove encryption, reset a device or reinstall an operating system before seeking advice. These actions can overwrite recoverable information or remove metadata needed to locate the encrypted volume. Keep any recovery keys, password manager records, old devices and documentation available for the technician.
Confidentiality also has legal limits. A legitimate service provider may have to comply with a valid court order, warrant or other legal requirement. That is different from voluntary disclosure. A professional provider should not access, share or use customer data outside the recovery service without a lawful reason or your authority.
Organisations handling personal information should consider their own obligations under the Privacy Act and any contractual duties owed to customers. If a lost drive contains personal data and has been out of your control, your internal privacy or legal team may need to assess whether the incident requires further action. Data recovery can restore access, but it does not automatically remove any broader breach-management responsibility.
How to protect your confidentiality during recovery
The best time to set expectations is before the device changes hands. Tell the recovery provider that the data is confidential and identify any requirements that apply, such as an NDA, restricted contacts, named collection authorities, or a requirement to return all media directly to a particular staff member.
Remove nothing from the device and avoid running repair utilities, recovery software or repeated restart attempts if the media is failing. These actions are not privacy protections, and they can reduce the chance of a complete recovery. Instead, isolate the device, record what happened, and provide a clear history of the failure.
Once your data has been returned, copy it to your own secure storage promptly and confirm that the important folders are present. Ask the provider to explain its retention and secure deletion process for working copies. For high-sensitivity matters, request written confirmation when temporary recovery data has been removed in line with the agreed process.
Your files do not become less private because a drive has failed. Choose a recovery provider that treats confidentiality as part of the technical service, ask direct questions before work starts, and make sure the recovery process is documented well enough for you to trust it.
